Spyware.GoldenEye
Threat Scorecard
EnigmaSoft Threat Scorecard
EnigmaSoft Threat Scorecards are assessment reports for different malware threats which have been collected and analyzed by our research team. EnigmaSoft Threat Scorecards evaluate and rank threats using several metrics including real-world and potential risk factors, trends, frequency, prevalence, and persistence. EnigmaSoft Threat Scorecards are updated regularly based on our research data and metrics and are useful for a wide range of computer users, from end users seeking solutions to remove malware from their systems to security experts analyzing threats.
EnigmaSoft Threat Scorecards display a variety of useful information, including:
Popularity Rank: The ranking of a particular threat in EnigmaSoft’s Threat Database.
Severity Level: The determined severity level of an object, represented numerically, based on our risk modeling process and research, as explained in our Threat Assessment Criteria.
Infected Computers: The number of confirmed and suspected cases of a particular threat detected on infected computers as reported by SpyHunter.
See also Threat Assessment Criteria.
| Threat Level: | 80 % (High) |
| Infected Computers: | 129 |
| First Seen: | July 24, 2009 |
| Last Seen: | January 9, 2026 |
| OS(es) Affected: | Windows |
The detection of Spyware.GoldenEye on your system indicates a potential security threat that requires immediate attention. This type of malware is designed to secretly monitor and collect sensitive information from your computer, compromising your privacy and security. It is essential to understand the nature of this threat and take prompt action to remove it and prevent future infections.
Table of Contents
What Is Spyware.GoldenEye?
Spyware.GoldenEye is a type of spyware that is designed to stealthily infiltrate a computer system and gather sensitive information without the user's knowledge or consent. This can include personal data, login credentials, browsing history, and other confidential information. The primary goal of spyware is to exploit this information for malicious purposes, such as identity theft, financial fraud, or targeted advertising.
How Spyware.GoldenEye Operates
Spyware.GoldenEye, like other spyware, typically operates by installing itself on a computer system through exploited vulnerabilities, drive-by downloads, or social engineering tactics. Once installed, it can hide in the background, monitoring and collecting data, and transmitting it to its command and control servers. Spyware can also modify system settings, disable security software, and create backdoors for remote access, making it challenging to detect and remove.
Symptoms of Infection
Identifying a spyware infection can be challenging, as it often operates stealthily. However, some common symptoms may indicate the presence of Spyware.GoldenEye or other malware. These can include slow system performance, unexpected pop-ups, changed browser settings, and unfamiliar programs or toolbars. Additionally, you may notice that your computer is behaving erratically, or you are experiencing unusual network activity.
- Unexplained changes to your system or browser settings
- Pop-ups, ads, or other unwanted content
- Slow system performance or crashes
- Unfamiliar programs or toolbars
- Increased network activity or data usage
How to Remove Spyware.GoldenEye
- Boot your computer in Safe Mode with Networking to prevent the malware from loading and to allow for a more effective removal process.
- Use a reputable anti-malware tool, such as SpyHunter, to perform a full scan of your system and detect any malware, including Spyware.GoldenEye.
- Uninstall any suspicious programs or software that you do not recognize or no longer need, as these could be related to the spyware infection.
- Reset your web browsers, including Chrome, Firefox, and Edge, to their default settings to remove any malicious extensions or settings changes.
- Reboot your computer and perform another scan with your anti-malware tool to ensure that all traces of the malware have been removed.
Conclusion
Removing Spyware.GoldenEye and other types of spyware requires a combination of technical knowledge, the right tools, and caution. By understanding how spyware operates and taking the necessary steps to remove it, you can protect your personal data and prevent future infections. It is crucial to remain vigilant and proactive in maintaining your computer's security, including keeping your operating system and software up to date, using strong antivirus software, and being cautious when clicking on links or downloading attachments from unknown sources.
Aliases
15 security vendors flagged this file as malicious.
| Antivirus Vendor | Detection |
|---|---|
| AVG | Logger.CYT |
| AhnLab-V3 | Win-AppCare/Xema.970752 |
| Antiy-AVL | Monitor/Win32.GoldenEye.gen |
| Comodo | ApplicUnsaf.Win32.Monitor.GoldenEye.c |
| BitDefender | Application.Generic.192090 |
| Kaspersky | not-a-virus:Monitor.Win32.GoldenEye.c |
| Panda | Application/GoldenEye |
| AVG | Generic2.OOS |
| Fortinet | Keylog/GoldenEye |
| Prevx1 | High Risk Worm |
| McAfee-GW-Edition | Riskware.GoldenEye.401.4 |
| AntiVir | SPR/GoldenEye.401.4 |
| F-Secure | Monitor.Win32.GoldenEye.401 |
| Comodo | ApplicUnsaf.Win32.Monitor.GoldenEye.401 |
| Kaspersky | not-a-virus:Monitor.Win32.GoldenEye.401 |
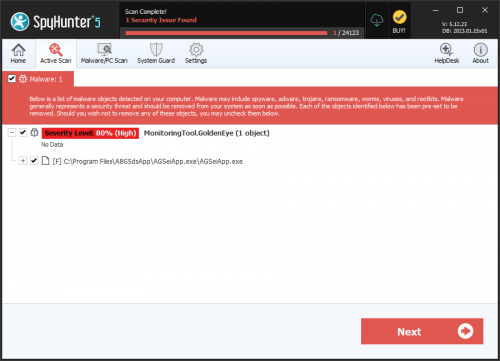
SpyHunter Detects & Remove Spyware.GoldenEye
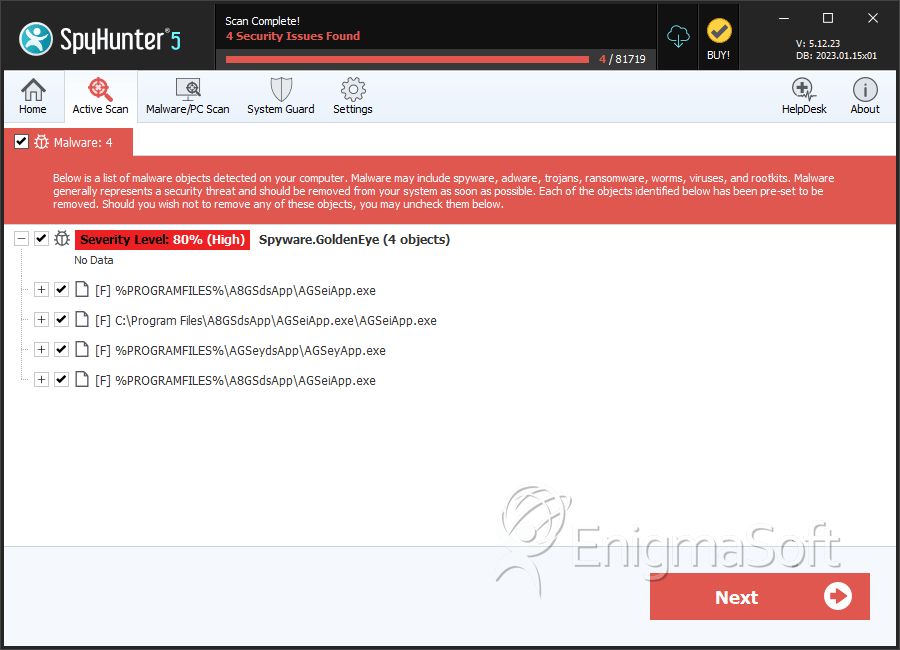
File System Details
| # | File Name | MD5 |
Detections
Detections: The number of confirmed and suspected cases of a particular threat detected on
infected computers as reported by SpyHunter.
|
|---|---|---|---|
| 1. | AGSeiApp.exe | f1cbdd2be9748d9e75d69142c550feb0 | 18 |
| 2. | AGSeyApp.exe | 4af8cc3aa21d6d6fe6682e48a6aaf176 | 3 |
Analysis Report
General information
| Family Name: | Spyware.GoldenEye |
|---|---|
| Signature status: | No Signature |
Known Samples
Known Samples
This section lists other file samples believed to be associated with this family.|
MD5:
91fa66750c92e601e58e0c892212d01e
SHA1:
18799cc09bea100b80b398a61e8894f88d77da74
SHA256:
DB37771F4445CD3ECFE725ED1994484CE654CA42BE833D6C08B9CB6E703F2758
File Size:
966.66 KB, 966656 bytes
|
Windows Portable Executable Attributes
- File doesn't have "Rich" header
- File doesn't have debug information
- File doesn't have exports table
- File doesn't have relocations information
- File doesn't have security information
- File is 32-bit executable
- File is either console or GUI application
- File is GUI application (IMAGE_SUBSYSTEM_WINDOWS_GUI)
- File is Native application (NOT .NET application)
- File is not packed
Show More
- IMAGE_FILE_DLL is not set inside PE header (Executable)
- IMAGE_FILE_EXECUTABLE_IMAGE is set inside PE header (Executable Image)
File Icons
File Icons
This section displays icon resources found within family samples. Malware often replicates icons commonly associated with legitimate software to mislead users into believing the malware is safe.
Windows PE Version Information
Windows PE Version Information
This section displays values and attributes that have been set in the Windows file version information data structure for samples within this family. To mislead users, malware actors often add fake version information mimicking legitimate software.| Name | Value |
|---|---|
| File Version | 4.01.0001 |
| Internal Name | AGSeApp |
| Original Filename | AGSeApp.exe |
| Product Name | Application |
| Product Version | 4.01.0001 |
File Traits
- vb6
- x86
Windows API Usage
Windows API Usage
This section lists Windows API calls that are used by the samples in this family. Windows API usage analysis is a valuable tool that can help identify malicious activity, such as keylogging, security privilege escalation, data encryption, data exfiltration, interference with antivirus software, and network request manipulation.| Category | API |
|---|---|
| Other Suspicious |
|